Dual-Screen POS Security and PCI Compliance Tips
- Threat model and physical/software risks for two-sided checkout hardware
- Common physical attack vectors and mitigations
- Firmware integrity, secure boot and update controls
- Customer privacy, PIN exposure and display placement
- Regulatory mapping: PCI frameworks and industry standards for double-display systems
- PCI DSS, P2PE and PTS considerations
- EMV certification and secure PIN entry
- Aligning to NIST/ISO for cryptographic and supply-chain controls
- Procurement and deployment best practices to achieve compliance and operational resilience
- Specification checklist for RFPs and vendor evaluation
- On-site hardening, network segmentation and POS environment controls
- Encryption key management and remote update governance
- Manufacturing controls, integration and FAVORPOS deployment guidance
- Design decisions that reduce attack surface and support auditing
- Testing, certification and post-market vulnerability handling
- FAVORPOS solutions: capabilities, products and enterprise support
- Frequently Asked Questions
- Does a customer-facing second display make PCI compliance harder?
- What certifications should be required in procurement documents for two-sided terminals?
- How should encryption keys for customer-facing payment devices be managed?
- Are there installation best practices to prevent PIN observation on dual-display checkouts?
- What post-deployment controls help maintain compliance over time?
High-density Dual-facing checkout terminals and customer-display checkout units require a combined approach of hardware tamper-resistance, end-to-end cryptographic protection, and operational controls to satisfy PCI standards and reduce theft and fraud risk. This enterprise guide explains threat models for two-sided checkout devices, maps specific controls to PCI DSS, PCI PTS and P2PE frameworks, and prescribes procurement, integration, and lifecycle practices for retailers and hospitality operators. Actionable vendor selection criteria, deployment checklists, and a comparative table (single-facing vs. customer-visible dual-display hardware) support procurement decisions; authoritative standards referenced include the PCI Security Standards Council, NIST, and ISO.
Threat model and physical/software risks for two-sided checkout hardware
Common physical attack vectors and mitigations
Enterprise buyers should assess how a customer-facing second display changes the physical attack surface. Adversaries may attempt skimming devices attached to customer-facing bezels, covert cameras capturing PIN entry, or swap attacks against peripheral cables. Specify tamper-evident housings, sealed connectors, and integrated PIN pads with tamper sensors. Procure units certified for PIN transaction security (PTS) where PIN entry is required; these devices include anti-tamper responses and tamper logging to meet cardholder data protections.
Firmware integrity, secure boot and update controls
Firmware compromise is a principal vector for persistent intrusions. Require secure boot chains, signed firmware updates, and hardware-backed key storage such as a Trusted Platform Module (TPM) or secure element. Update policies must include cryptographic signature checks and validation logs. Vendors should provide detailed firmware provenance and revocation procedures to support incident response and forensic analysis.
Customer privacy, PIN exposure and display placement
Two-sided display units improve transparency for the cardholder but can inadvertently expose PIN entry or transaction metadata. Use ergonomics-driven install guidance to minimize sightlines to PIN pads and implement display modes that redact sensitive values. For environments accepting EMV chip-and-PIN, ensure the entry device meets PIN entry device standards and that on-screen customer prompts do not reveal PAN fragments beyond what is required for verification.
Regulatory mapping: PCI frameworks and industry standards for double-display systems
PCI DSS, P2PE and PTS considerations
Dual-display checkout solutions must be analyzed across relevant PCI programs. The PCI Security Standards Council defines requirements for PCI DSS (data environment controls), P2PE (encryption from point-of-interaction to decryptor) and PTS (secure PIN entry and tamper resistance). Buyers should verify whether a proposed two-facing terminal supports P2PE or uses validated PTS hardware when PIN entry occurs on the customer side. If P2PE is implemented, the device should be listed in approved solutions or integrated into a validated solution set.
EMV certification and secure PIN entry
EMV compliance ensures proper card interaction for chip transactions; for PIN-based flows, the hardware must comply with PCI PTS and have documented EMV test reports. Demand vendor-provided certification references and test reports, and include acceptance criteria in procurement contracts to ensure equipment remains within scope of EMV and PCI program requirements during firmware revisions.
Aligning to NIST/ISO for cryptographic and supply-chain controls
While PCI prescribes cardholder data protections, aligning cryptographic algorithms and key lifecycle to NIST recommendations improves future-proofing (e.g., using AES-GCM for authenticated encryption, secure RNGs, and FIPS-validated modules when required). Supply chain and quality controls should reference ISO standards for quality management (ISO 9001) and information security (ISO/IEC 27001) to reduce risks of counterfeit components or unauthorized firmware insertion.
Procurement and deployment best practices to achieve compliance and operational resilience
Specification checklist for RFPs and vendor evaluation
Procurement teams should include a security appendix in RFPs that lists required certifications (PCI PTS, P2PE compatibility, EMV level tests), secure boot capability, hardware root of trust, tamper detection, and detailed support SLAs for firmware security patches. Insist on documented vulnerability disclosure programs, secure development lifecycle (SDL) evidence, and third-party penetration test results for the device OS and integrated payment application.
On-site hardening, network segmentation and POS environment controls
Deployment playbooks must mandate network segmentation for POS endpoints, allow only approved outbound connections, and use application whitelisting where possible. Secure configuration templates should disable unused services, enforce encrypted management channels, and set strict administrative access controls. Integrate device attestation checks during daily health checks to detect unauthorized modifications.
Encryption key management and remote update governance
Key management is central to maintaining P2PE and overall cryptographic integrity. Implement centralized key lifecycle processes that include secure generation, escrow, rotation, and destruction, ideally using HSM-backed services. Remote update workflows should require signed artifacts and staged rollouts with rollback plans and integrity verification to reduce risk of failed updates introducing vulnerabilities.
| Aspect | Single-facing checkout terminal | Customer-facing dual-display / two-sided terminals |
|---|---|---|
| Customer PIN privacy | PIN pad often shielded but customer may need to turn to view receipts | Requires careful PIN pad placement and display modes to avoid exposure; can enhance receipt visibility without PIN disclosure |
| Attack surface (physical) | Lower visible attack points, simpler bezel design | Increased external surfaces; demands tamper-evident design and sealed connectors |
| Regulatory readiness | Meets standard POS certification pathways; simpler PTS validation scope | Must demonstrate PTS for customer-side PIN entry and P2PE compatibility where required |
| Transaction transparency | Limited customer-facing transaction feedback | Improves customer verification and reduces disputes when configured correctly |
| Recommended for EMV PIN workflows | Suitable when PIN pad is properly integrated | Suitable if device carries PTS certification and follows PCI P2PE guidance |
Manufacturing controls, integration and FAVORPOS deployment guidance
Design decisions that reduce attack surface and support auditing
Device makers and integrators should favor integrated customer displays that share a sealed chassis with the PIN entry device to reduce cable-interception risks. Modular add-ons increase flexibility but require stricter connector security and authenticated pairing. Build-for-audit designs include tamper logs accessible to forensic teams, immutable update records, and hardware-backed device identifiers to support asset inventory reconciliation.
Testing, certification and post-market vulnerability handling
Reliable suppliers publish test evidence: PTS reports, EMV Level 2/3 results, and P2PE validation where applicable. Post-market vulnerability handling must include responsible disclosure timelines, rapid patch distribution mechanisms, and clear rollback procedures. Industry references for secure software practices such as OWASP guidance are useful for web-based POS applications that run on dual-display units.
FAVORPOS solutions: capabilities, products and enterprise support
As an experienced provider, FAVORPOS develops point-of-sale hardware and peripheral ecosystems designed for enterprise deployments that demand both customer-facing experiences and robust security. Our product lines include multifunction checkout terminals with customer displays, handheld payment devices, price checking kiosks, and peripherals such as thermal printers and cash drawers. We deliver OEM and ODM services, enabling custom chassis sealing, secure element integration, and firmware signing tailored to a client’s compliance scope.
Our engineering team implements secure supply-chain controls and quality management aligned with ISO practices while supporting PCI program requirements. FAVORPOS offers POS system integration packages that include device attestation, managed firmware updates, and lifecycle support to minimize compliance drift. For hospitality and retail chains, these services reduce deployment complexity and provide demonstrable evidence for audits and merchant level assessments.
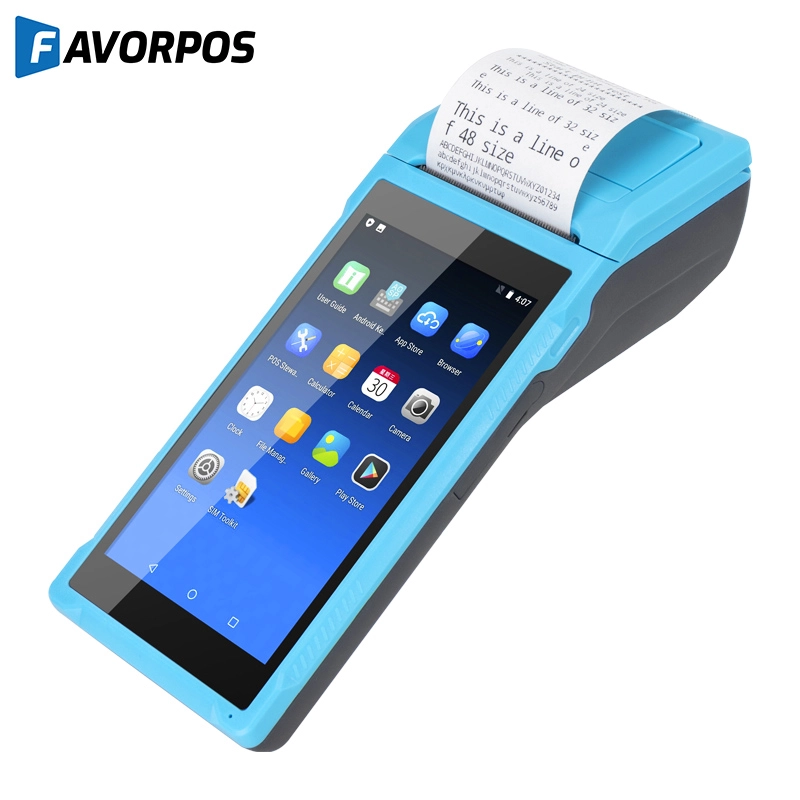
Specific product advantages include hardened handheld terminals for line-busting and mobile checkout, dual-display counter systems engineered for privacy-aware PIN entry, compact price checkers for shelf-edge validation, high-reliability thermal printers for receipt integrity, and robust cash drawer designs. These elements are designed to interoperate and support centralized key management, secure boot, and encrypted communications to payment processors and gateways.
Frequently Asked Questions
Does a customer-facing second display make PCI compliance harder?
Adding a customer display increases the device’s visible surface and potentially the attack vectors, but compliance difficulty depends on whether PIN entry is exposed on the customer side. If PIN entry occurs on a customer-facing device, require PCI PTS certification and, where applicable, P2PE support. Proper hardware selection, installation controls, and documented update processes mitigate incremental compliance complexity.
What certifications should be required in procurement documents for two-sided terminals?
Specify PCI PTS for PIN devices, EMV Level test evidence, and P2PE compatibility if using point-to-point encryption. Additionally, request vendor evidence of secure development practices, vulnerability disclosure policies, and independent penetration testing. Reference to NIST cryptographic baselines and ISO quality management documentation strengthens vendor accountability.
How should encryption keys for customer-facing payment devices be managed?
Keys should be generated and stored in HSM-backed systems where possible, with defined rotation schedules and secure escrow. Key injection processes must be documented and controlled, preferably via certified key injection facilities or vendor-managed injection services that preserve chain of custody and provide audit logs.
Are there installation best practices to prevent PIN observation on dual-display checkouts?
Yes. Position devices to minimize direct sightlines to PIN entry, use privacy shields or angled mounts, and configure the customer display to suppress sensitive data where unnecessary. Include staff training on supervising transactions and rapidly reporting tamper indicators.
What post-deployment controls help maintain compliance over time?
Implement continuous monitoring of device health, enforce signed firmware updates with staged rollouts, maintain a device inventory with attestation checks, and define SLA-driven patch timelines with vendors. Regular internal audits and evidence-ready documentation simplify external PCI assessments.
Contact FAVORPOS or view our product catalog to evaluate secure dual-display checkout options, handheld terminals, thermal printers, and peripherals for compliant enterprise deployments.

FAVORPOS dual screen POS terminals deliver fast, reliable checkout performance for retail and hospitality businesses. Built by our commercial pos terminal manufacturer, these thin-profile systems streamline transactions while maximizing counter space—trusted by checkout pos systems factory operations worldwide.
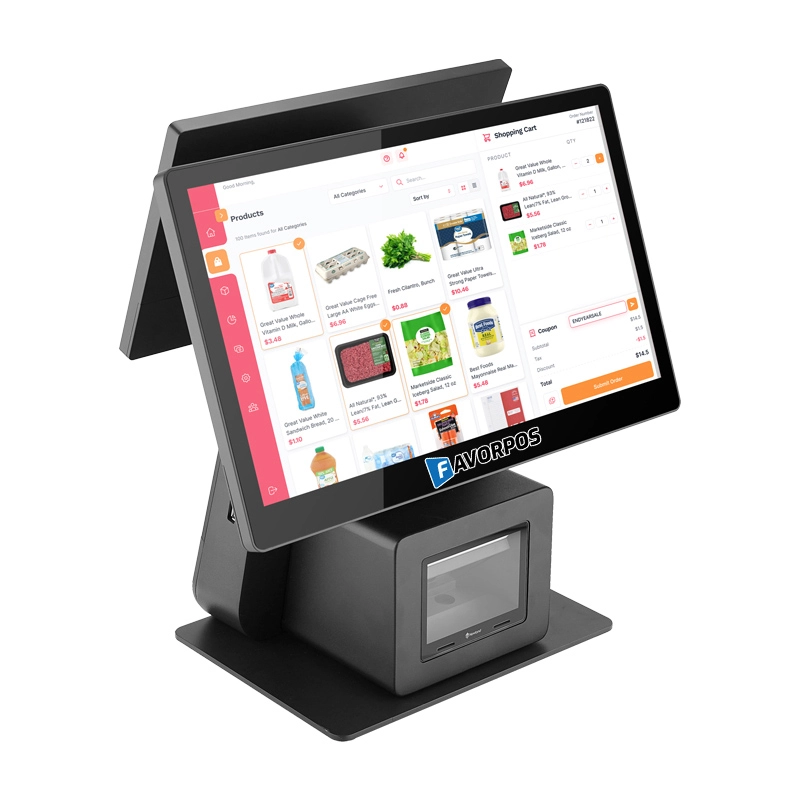
FAVORPOS: Your leading dual screen POS factory and manufacturer. Our desktop POS with barcode scanner offers 15.6/11.6 client screen options and OS flexibility. Get reliable, efficient dual screen POS with barcode scanner solutions directly from us.
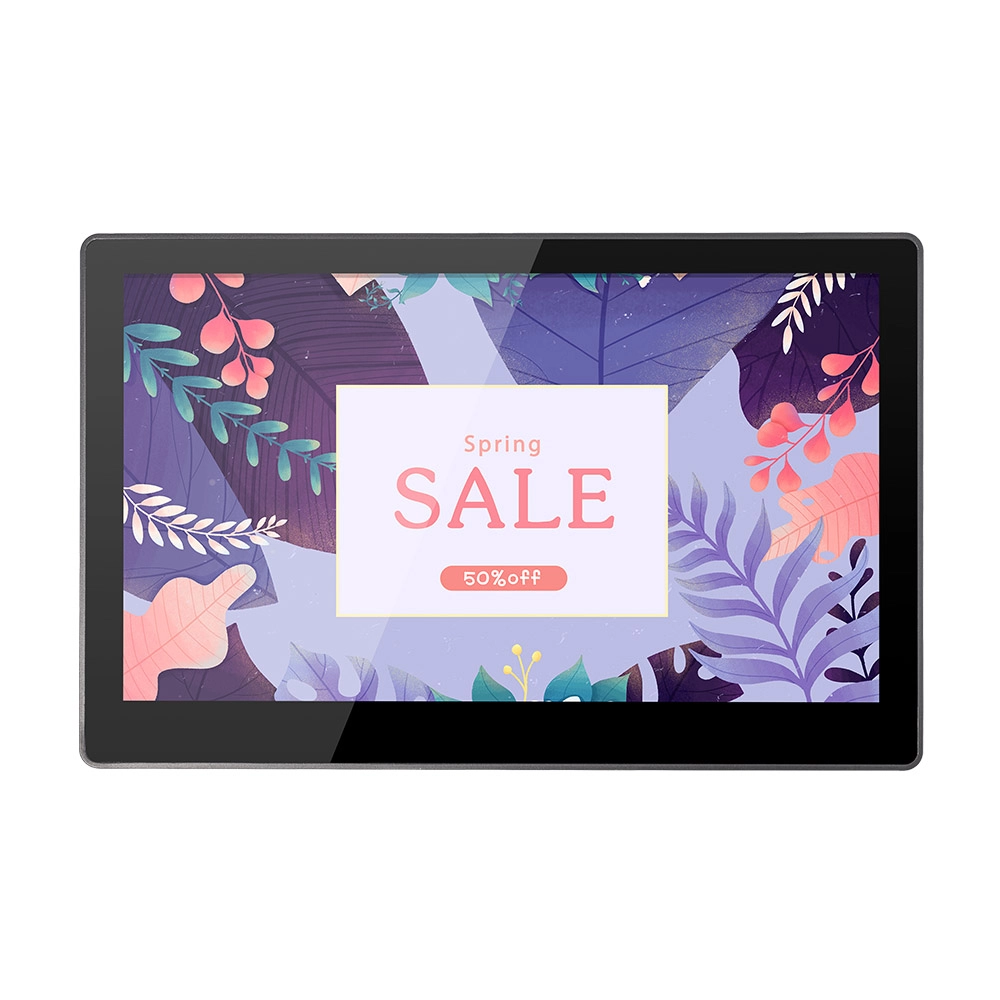
FAVORPOS 11.6-inch capacitive touchscreen, specifically designed for POS machines to deliver a seamless and responsive user experience. This high-definition display offers vibrant visuals and crystal clear clarity, making it easy for staff to navigate through transactions efficiently. The capacitive technology ensures quick and accurate touch recognition, reducing wait times and enhancing customer satisfaction. Built to withstand the rigors of daily use, this touchscreen is perfect for retail and hospitality environments.


Copyright © 2025 Favorpos All Rights Reserved.
